
In late 2025, I had the privilege of being welcomed into the financial sector — banking and fintech — first as an Information Security Officer (ISO) and now as VP, Corporate Security Officer, covering the full converged security spectrum. Small and community banks rarely have the staff or budget to mature their security program at the rate of risk, but they carry a lot of the same regulatory expectations. As I’ve gotten to know my new peer group, I wanted to give back with a small “bank” of free, open resources — tools, references, and the occasional metric — pulled from 35+ years across converged security. Since I’m a converged security advocate, expect the mix to span governance, cyber, physical, personnel, fraud, and investigations, not just one lane. And no, the majority of this content is not AI generated, it from real world experience and implementation. But I do use AI on some items as a starting point when I don’t understand a particular domain or to review my existing content to better it for my audience.
Before you dive in: my Converged Security Definitions page defines 57 of the terms used across these tools and policies — worth a bookmark if your team doesn’t share a common vocabulary yet.
Note: This page and associated resources are not endorsed by Ciera Bank, my clients, TBA, TBA ISAO, ICBA, CB ISAO/ISAC, ABA or any other organization that I might provide resources for the betterment of the banking industry.
Governance
Converged Security Governance Self-Assessment
A simple small-business self-assessment — built with a small bank in mind — to baseline where your governance program stands today.
Security Metrics for Banks
A Top 25 list of practical governance metrics — simple, boardroom-ready measures to challenge (and maybe scare) your BoD, senior leadership, and BSO/ISO leadership.
CRI Self-Assessment PowerBI Dashboard — Coming Soon
*Supplier Tool
A PowerBI dashboard for scoring the Cyber Risk Institute’s CRI Profile self-assessment, in development by Mitchell of Secure Metrics. Check back soon.
Supplier & Customer Due Diligence
A one-page policy for vetting suppliers and customers — the converged security side of third-party risk management.
Coming Soon
A new resource for this category is in development.
Coming Soon
A new resource for this category is in development.
Business Continuity & Disaster Recovery (BC/DR)
Business Continuity & Disaster Recovery (BCP/DRP)
A one-page policy defining security’s role in business continuity and disaster recovery planning — a standing exam question for every bank.
Coming Soon
A new resource for this category is in development.
Coming Soon
A new resource for this category is in development.
Information / Cyber Security
R-SAT Quantification Tool
A scoring workbook that quantifies your bank’s completed R-SAT (Ransomware Self-Assessment Tool) responses into a baseline risk score.
Non-Public Information (NPI/PII) Security Policy
A one-page NPI/PII security policy covering data classification, access controls, storage and transmission requirements, and breach response.
Minimum Cyber Security Policy (CIS 18 Critical Controls)
A one-page minimum cyber security policy aligned to the CIS 18 Critical Controls — the essential controls every organization should have in place.
Email Security Policy
A one-page email security policy covering acceptable use, phishing awareness, attachment handling, BEC risks, and retention requirements.
User IDs & Login Security Policy
A one-page user ID and login security policy covering password standards, MFA requirements, shared account prohibitions, and account review schedules.
Laptop, Desktop & Mobile Device Security
A one-page policy covering endpoint security expectations for laptops, desktops, and mobile devices — encryption, patching, and loss/theft response.
Physical Security
Physical Security Policy
A one-page physical security policy covering perimeter controls, access management, visitor handling, key and badge control, and facility security.
Visitor Management
A one-page policy for logging, badging, and escorting visitors — branch lobbies and back-office alike.
Active Assailant Response Policy
One-page active assailant response policy covering definitions, Run-Hide-Fight options, and individual, leadership, and security team requirements.
Emergency Evacuation & Shelter-in-Place
A one-page emergency evacuation and shelter-in-place policy covering assembly points, communication protocols, accountability, and special needs.
Coming Soon
A new resource for this category is in development.
Coming Soon
A new resource for this category is in development.
Personnel Security
Simon Osamah’s Decision Decks
*Supplier Tool
Scenario-based training decks for personnel security discussions, built by my good friend Simon Osamah — a great source when you need realistic training scenarios.
Personnel Security Policy
A one-page personnel security policy covering the baseline expectations that apply to every employee, from hire to termination.

Background Check Policy
One-page background check policy covering minimum screening elements, scope, and requirements for HR, legal, security teams, and all personnel.

Insider Threat Management
A one-page policy for identifying and managing insider threat risk — especially relevant where a handful of employees can move real money.
Recruiting & Onboarding
A one-page policy covering the security side of recruiting and onboarding new hires.
Termination & Offboarding
A one-page termination and offboarding security policy covering access revocation timelines, equipment return, and exit interview requirements.
Robbery Chain of Survival
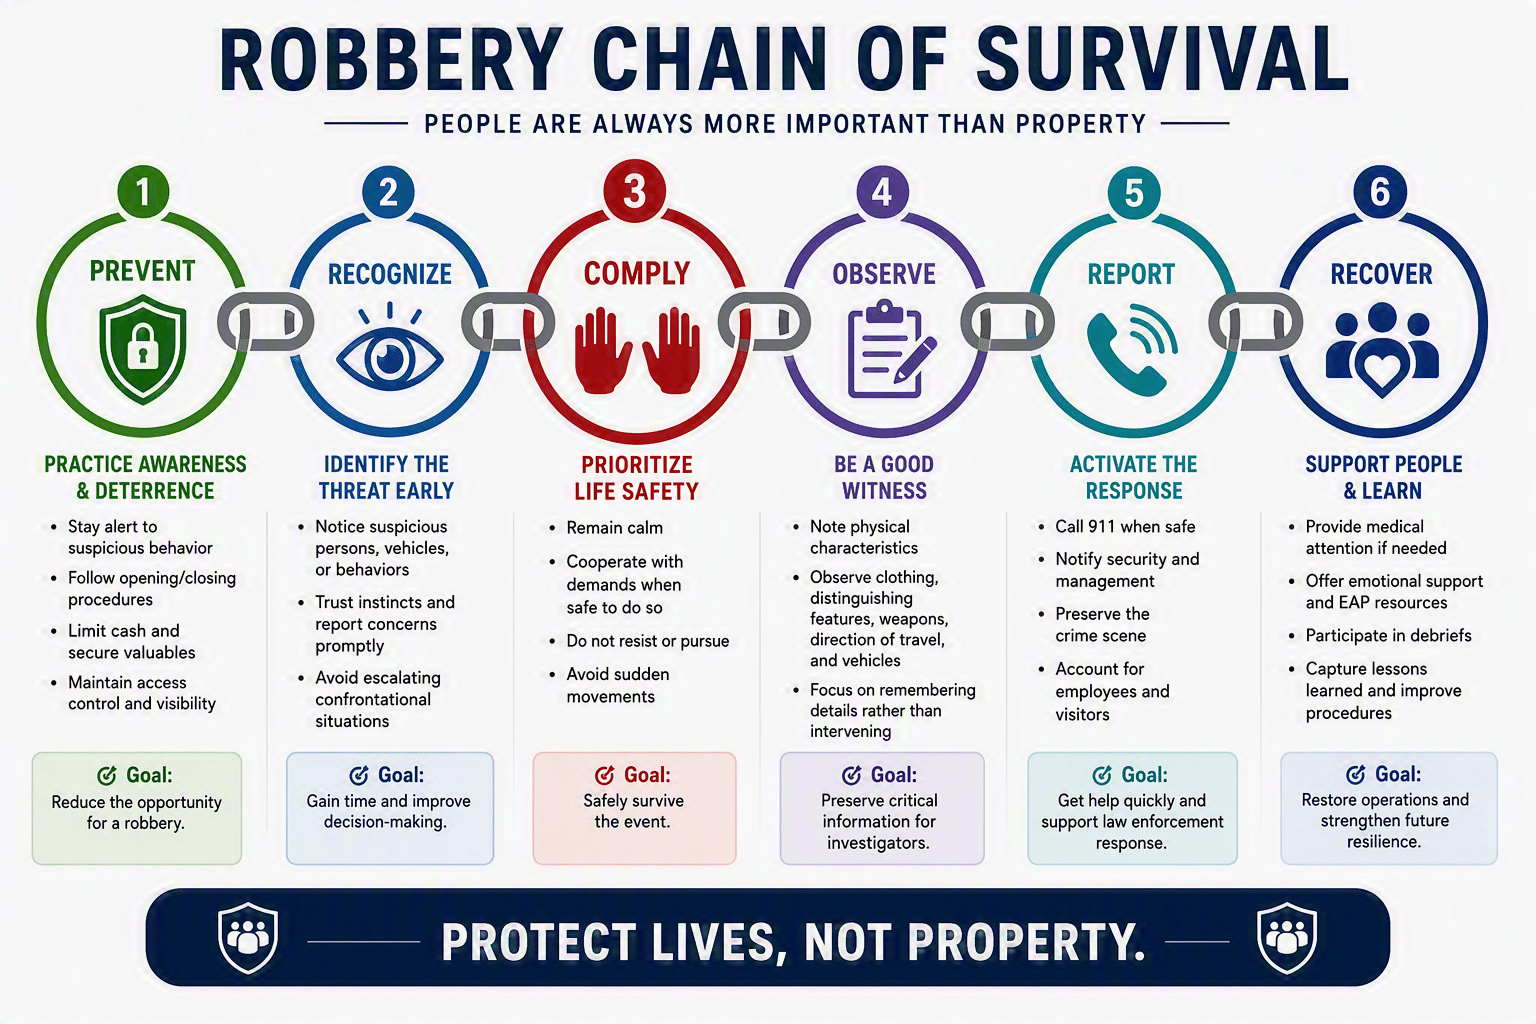
A “Chain of Survival” visual for bank robbery response, modeled on the familiar CPR/AED/First Aid Chain of Survival framework — each link represents a critical action from prevention through recovery. Created by Microsoft Copilot based on Jim’s guidance.
Coming Soon
A new resource for this category is in development.
Coming Soon
A new resource for this category is in development.
Fraud
My Business Email Has Been Compromised — What Are My First Steps?
First-step guidance after a Business Email Compromise: how to contain the breach, who to notify, and what to fix across people, process, and technology.
Handling Cash & Checks
A one-page policy covering the security controls around handling cash and checks — as close to teller-line guidance as a one-pager gets.

Guarding HR Recruitment from Scams – Reference Tool
A quick-reference guide built for HR and recruiting teams — spot the red flags in fake job postings, candidate impersonation, and reference-check fraud before they cost you a bad hire. Drawn from the same fraud-awareness class I teach, reframed for the recruiter’s seat instead of the job seeker’s.
Investigations
Investigations: Internal vs. External Resources
Should your organization investigate internally or bring in outside professionals? This versus doc covers the pros, cons, and critical considerations.
Security Investigations Policy
A one-page policy setting expectations for how internal security investigations get opened, run, and documented.
Reporting Security Incidents
A one-page policy defining what counts as a reportable security incident and how to escalate it.
Missing Something?
This bank of resources will keep growing. If you have a suggested addition or a story about how you used one of these, let me know.